Privileged Access at the IT/OT Boundary: What Breaks When Enterprise PAM Meets the Factory Floor
About This Session
As manufacturing, defense production, and critical infrastructure environments modernize, privileged access no longer stays neatly divided between enterprise IT and operational technology. Engineers, vendors, service accounts, shared workstations, remote access tools, break-glass users, and automation can all create access pathways between corporate identity systems and plant-floor environments.
But many privileged access management programs were designed around enterprise assumptions: centralized directories, clear account ownership, routine credential rotation, standard logging, and systems that can tolerate downtime. Those assumptions can break down in operational environments where safety, uptime, legacy systems, vendor dependencies, and production continuity shape every control decision.
This session examines the privileged access gaps that emerge in IT/OT convergence zones. Rather than treating PAM as an enterprise-only discipline, the talk explores how organizations can evaluate privileged access risk across manufacturing and industrial environments without blindly applying corporate IT controls to the plant floor.
Topics include privileged account ownership, vendor and remote access pathways, engineering workstation access, service and shared accounts, emergency access, auditability, and governance blind spots when OT assets are not represented in enterprise identity models.
Attendees will leave with practical questions and a maturity checklist for assessing privileged access risk across IT/OT convergence zones while preserving safety, reliability, and production continuity.
Speaker
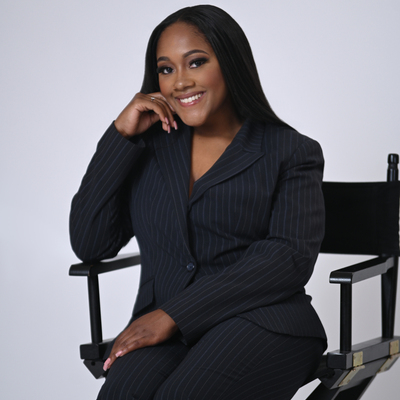
Victoria Galloway
Cybersecurity Program Manager - Southern Company
Victoria Galloway is a cybersecurity program leader focused on identity governance, privileged access management, and enterprise security transformation in complex environments. Her work spans IAM, PAM, governance, compliance, and cybersecurity program execution, with a focus on translating technical access risk into operational and executive decision-making. She is PMP-certified, holds a master’s degree in cybersecurity from UC Berkeley, and is passionate about helping organizations strengthen identity and privileged access controls as technology environments become more interconnected, automated, and operationally critical.