



Abdul Khadir Mahamed
OT Cybersecurity Architect - Estee Lauder Companies
Abdul Khadir Mahamed is an Information Technology (IT) , Operational Technology (OT) and Industrial Control Systems (ICS) cybersecurity professional with over 13 years of experience designing, implementing, and governing cybersecurity programs across global manufacturing environments. Expertise includes secure remote access, IT/OT convergence security, OT asset intelligence, vendor risk management, industrial network security, vulnerability management, and cybersecurity governance. Led initiatives supporting manufacturing plants, research and development facilities, distribution centers, and critical infrastructure operations across multiple global regions.
Sessions
-
Why Securing the OT Value Chain Is the Next Critical Challenge for Global ManufacturersThursday, October 8, 2026
9:35 AM - 10:05 AM
Brad Nash
OTCRM SOC Supervisor - ExxonMobil
Brad Nash is the OTCRM Security Operations Center Supervisor – Americas, leading 24/7 monitoring and incident response for industrial operations and overseeing ICS External Network Connections (ENC) standards. With more than a decade across energy and financial services, he specializes in detection engineering, SOC automation, and IT–OT collaboration that protects safety-critical environments. He holds a B.S. in Network Communications & Management and an A.S. in Network & System Administration.
Sessions
-
Panel: Building a SOC That Can Defend Both IT and OTTuesday, October 6, 2026
1:30 PM - 2:15 PM
Brad Willet
OT Security Infrastructure Architect - UPS
Brad Willet is an OT Security Infrastructure Architect at UPS, where he focuses on securing and strengthening the operational technology environments that support one of the world’s largest and most complex logistics networks. His work sits at the intersection of cybersecurity, industrial infrastructure, and large-scale operations, addressing challenges such as OT asset visibility, infrastructure security, IT/OT convergence, and safely identifying and managing industrial assets without disrupting critical business operations. Brad brings a practitioner’s perspective shaped by working across a global enterprise with thousands of facilities and decades of operational technology.
Sessions
-
Panel: From Warning to Action - Defending Critical Infrastructure in Real TimeTuesday, October 6, 2026
1:30 PM - 2:15 PM
Eric Devoy
OT Security Architect - Grainger
Eric Devoy is an OT cybersecurity and digital transformation leader with 25+ years of experience securing industrial operations and enabling digital transformation. At Grainger, he leads OT security for highly automated distribution centers, driving strategy, governance, segmentation, secure remote access, monitoring, incident response, vulnerability management, and reference architectures for automation and robotics. Previously at bp, he led global OT security strategy and architecture across 150+ industrial sites, including refineries, offshore platforms, renewables, and EV charging infrastructure. His expertise spans OT cybersecurity, ICS/SCADA, IT/OT architecture, industrial automation, cloud and edge platforms, and organizational transformation.
Sessions
-
Securing Connected OT Across Cloud, Vendors, Robotics, and AIWednesday, October 7, 2026
9:00 AM - 9:35 AM
Joel Pixley
Cybersecurity Specialist - CISA
Joel Pixley is a senior cybersecurity leader with more than 11 years of experience protecting critical infrastructure and high-value federal systems. He currently serves as a Cybersecurity Specialist at the Department of Homeland Security’s Cybersecurity and Infrastructure Security Agency (CISA), where he leads the Validated Architecture Design Review (VADR) and High Value Asset (HVA) assessment programs. In this role, he guides the full lifecycle of 80–100 national-scale cybersecurity assessments annually across all 16 critical infrastructure sectors. Before joining CISA, Pixley spent nearly nine years protecting operational grid systems at Omaha Public Power District, advancing from intern to Senior Grid Operations Technology Engineer. He helped engineer and secure the industrial control networks supporting energy delivery to more than 855,000 customers while maintaining 99.8% uptime and full NERC CIP compliance with zero violations. A CISSP-certified professional, Pixley brings deep expertise in ICS/OT cybersecurity, NIST frameworks, Zero Trust architecture, incident response, and cyber resilience. He has led federal and cross-functional teams, overseen multimillion-dollar cybersecurity operations, and advised executive leaders across civilian agencies, energy providers, and national laboratories. He is also passionate about mentoring future cybersecurity professionals and strengthening the next generation of cyber leaders.
Sessions
-
Fortifying the Front Lines: Public-Private Readiness for an OT CrisisWednesday, October 7, 2026
3:50 PM - 4:20 PM
Michelle Farr
VP, CISO - NXP Semiconductors
Michelle Farr is Global Chief Information Security Officer (CISO) and Vice President at NXP Semiconductors, where she runs security as a warning discipline, carrying the analytic tradecraft of the intelligence world into commercial practice so judgment arrives ahead of the incident. A Navy Mustang who earned her commission from the ranks and was among the first women to qualify as a Surface Warfare Officer while operating in an expeditionary warfare environment. She went on to serve across the Intelligence Community, including as Senior Advisor for human intelligence at ODNI. She chairs the Government Security Committee at XTAR and is completing doctoral research at Purdue on how institutions calibrate trust in algorithmic judgment. She has spent her career on the boundary where commercial enterprise meets national security obligation, and she has never worked it as a spectator.
Sessions
-
25 Years of Warning Signals: From OT to AITuesday, October 6, 2026
9:00 AM - 9:35 AM
Mike Holcomb
OT/ICS cybersecurity Consultant - UtilSec
Mike Holcomb is an independent OT/ICS cybersecurity consultant, educator, and content creator. Through UtilSec, he helps organizations secure critical infrastructure and industrial environments. Previously, he was a Fellow of Cybersecurity and Global OT/ICS Cybersecurity Lead for a global engineering company, working across power, rail, manufacturing, and refining. Mike founded BSidesICS/OT, holds a master’s in OT/ICS cybersecurity from SANS Technology Institute, and maintains certifications including CISSP, GICSP, GRID, GCIP, GPEN, GCIH, and ISA/IEC 62443. He received the 2025 SANS Difference Maker Award for ICS/OT Defender and the 2026 BEER-ISAC Community Builder Award for contributions to the OT/ICS cybersecurity community. Learn more at mikeholcomb.com.
Sessions
-
Can This Happen to Us? Using Free Resources to Turn OT Threat Awareness Into ActionWednesday, October 7, 2026
9:00 AM - 9:35 AM
Rina Rakipi
Operations Coordinator, Threat Hunting - CISA
Rina Rakipi is Operations Coordinator, Threat Hunting at the U.S. Cybersecurity and Infrastructure Security Agency (CISA).
Sessions
-
CISA Threat Briefing: Lessons From Recent Critical Infrastructure IncidentsTuesday, October 6, 2026
11:00 AM - 11:35 AM
Shery S Thomas
Enterprise Information Technology Officer - US Navy Installations Command
As the Enterprise Information Technology Officer, Mr. Thomas serves to deliver common, business and operational IT services as part of the overall IT service activity. He provides advice and vision on all matters that are IT-related and enables the business and operational functions of the CNIC enterprise by providing strategic and tactical support to leverage information technology to accomplish the CNIC mission and provide better ways to receive, process, visualize, distribute and leverage existing data and collectively position CNIC for the role of Shore Force integrator for a total workforce of over 49,000+ sailors, civilians, and contractors across 10 regions and 70 installations across the globe. This includes oversight of Network and System Security Operations, Enterprise Ashore Enclave, Enterprise/Infrastructure Services, Enterprise Information Management, Information Assurance/Security Services, Managed IT Services, Capital and Resource Allocation, and Public Safety Systems. Mr. Thomas is dual-hatted as the command intelligence officer responsible for aggregating all intelligence and threat information for the shore enterprise to include operations, facilities and environment, fleet and family support services, and resource management to enable assured command and control. He leads enabling cyber and intelligence for compute and store, collaboration, access control and identity management, data encryption and governance creating use of processes, tools, techniques and protocols for proactive network resiliency and command and control with data driven decision making.
Sessions
-
Panel: From Warning to Action - Defending Critical Infrastructure in Real TimeTuesday, October 6, 2026
1:30 PM - 2:15 PM
Aarin Buskirk
Consulting Engineer - Palo Alto Networks
Aarin Buskirk is a Consulting Engineer at Palo Alto Networks specializing in mobile security solutions across all global sectors. He has an extensive background building and securing routing infrastructure for service provider environments along with architecting the networking and security foundations of large-scale data centers. He previously specialized in networking and security within the intelligence community, supporting major defense contractors and government agencies in highly secured environments. He currently applies this broad expertise to help organizations, including those in the energy utility sector, protect and modernize their mission-critical mobile networks.
Sessions
-
Building Cyber Resilient OT Networks with 5GThursday, October 8, 2026
10:10 AM - 10:40 AM
Abhinav Agarwal
Sr Software Engineer - Rubrik
Abhinav Agarwal is an independent security researcher, software engineer at Rubrik, and open-source maintainer. His work focuses on vulnerability discovery, secure-by-default engineering, and the security maturity of widely deployed software. He has reported vulnerabilities across AI infrastructure, cloud platforms, cryptography, Linux/open-source components, and ICS/OT software, including issues coordinated through CISA and major vendors. He is a maintainer of sshfs and a collaborator in the libfuse ecosystem. His past talks include "Highly Scalable, Masterless, Distributed File System at Rubrik" at SDC 2025 and "SymEngine A Fast Symbolic Manipulation Library" at Scipy 2016
Sessions
-
When Vulnerability Discovery Outpaces Patching: AI-Assisted Research in ICS Protocol LibrariesThursday, October 8, 2026
12:00 PM - 12:30 PM
Ahmed Elmesiry
Principal Security Researcher - Fujitsu Research of Europe
Dr. Elmesiry is a principal security researcher at Fujitsu Research of Europe with a Ph.D. in information security and assurance. He has extensive experience in R&D, having held academic and industrial positions in various countries on six continents. He has worked on projects related to cybersecurity, IoT, and machine learning, and has received several awards for his work, including six best paper awards at international conferences. Dr. Elmesiry holds industrial certifications in the fields of managing networked systems and offensive cybersecurity from top tech companies. Dr. Elmesiry has also contributed to the field through patents, books, book chapters, and research papers.
Sessions
-
Breaking Threat Intel Silo: Cryptographic Threat Hunting in OT EnvironmentsTuesday, October 6, 2026
4:00 PM - 4:35 PM
Akshat Sinha
Site Reliability Engineer - Rubrik
A site-reliability engineer and security researcher focused on the infrastructure layer of AI and cloud-native systems. Akshat's work pairs hands-on vulnerability research with measurement — how engineering-maturity gaps in fast-adopted software become exploitable attack surface — with responsible disclosure across open-source AI platforms, language sandboxes, and infrastructure tooling.
Sessions
-
When Vulnerability Discovery Outpaces Patching: AI-Assisted Research in ICS Protocol LibrariesThursday, October 8, 2026
12:00 PM - 12:30 PM
Andrew Dettmer
Consultant (Industrial Cybersecurity) - Black & Veatch
Andrew is an Industrial Cybersecurity Consultant with Black & Veatch’s Industrial Cybersecurity Practice, specializing in advanced cybersecurity offerings for operational technology (OT) environments. Prior to joining Black & Veatch, he served as the industrial cybersecurity engineer for a nine-plant generation and transmission cooperative, where he spent nine years developing and leading a comprehensive cybersecurity program for plant control systems. Andy brings deep expertise in OT/ICS systems, regulatory compliance (including NERC CIP), and industry-recognized cybersecurity frameworks. He holds a B.S. in Computer Science and maintains several advanced certifications, including CISSP, GICSP, GRID, GCFA, and GCIP. He is the recipient of the 2025 Mike Assante Scholar Award.
Sessions
-
Preparing Your ICS Forensic ToolkitThursday, October 8, 2026
1:45 PM - 2:15 PM
Andrew Ginter
VP Industrial Security - Waterfall Security
At Waterfall Security Andrew leads a team of experts who work with the world's most secure industrial enterprises. Before Waterfall, he led the development of high-end industrial control system products at HP, of IT/OT middleware products at Agilent , and of the world's first industrial SIEM at Industrial Defender. Andrew is the author of three books on industrial / OT cybersecurity with 35,000 copies in print. He co-hosts the Industrial Security Podcast and contributes regularly to industrial security standards and best-practice guidance.
Sessions
-
Espionage vs. SabotageMonday, October 5, 2026
3:55 PM - 4:30 PM
Bernhard Hecker
CEO - Netop
Bernhard Hecker is the CEO leading Netop’s return to the market as a trusted provider of remote access and remote control solutions for defense, critical infrastructure, and public-sector organizations. A natural seer-builder, he brings clarity, strategic architecture, and a strong commitment to digital sovereignty to every decision. Bernhard has led product, strategy, and policy efforts at SUSE, Pluxee, Sympa, and Retarus, shaping secure systems and digital frameworks at the EU level. At Netop, he concentrates on rebuilding with integrity, resilience, and mission-critical reliability, ensuring that organizations operating in high-stakes environments can stay connected, secure, and in control.
Sessions
-
The Session You Didn't Know Was Open: Remote Access Blind Spots in Critical InfrastructureMonday, October 5, 2026
3:10 PM - 3:45 PM
Björn Gaworski-Dammann
Director of Product Management - Secomea
Björn Gaworski-Dammann is Director of Product Management at Secomea, where he shapes product strategy for industrial secure remote access and OT cybersecurity. With 20 years in enterprise software, including leading product management at CoreMedia, he has spent his career turning complex technical requirements into products people actually want to use. At Secomea, he works at the intersection of OT security, hybrid cloud architecture, and the realities of protecting critical infrastructure. Outside of work, Björn brings the same hands-on curiosity home: he is slowly turning his house into a full smart-home setup, wiring up IoT devices room by room and learning firsthand why securing connected devices is never as simple as it looks on a spec sheet. Based in Hamburg, Germany.
Sessions
-
From Secure Remote Access to Autonomous OT Security: How One Global Manufacturer Got It RightWednesday, October 7, 2026
11:00 AM - 11:35 AM
Brian "SchleiF" Schleifer
Director of Content, Events - SecurityWeek
Brian "SchleiF" Schleifer is Director of Content for SecurityWeek Events. He is a retired United States Air Force veteran, cybersecurity professional, podcast host and content leader. He previously served in senior cybersecurity engineering and leadership roles at Modern Technology Solutions, Inc. His experience includes cyber-physical and weapon systems security, security control assessment, cyber testing, risk management, and AI governance. He is pursuing a Doctor of Technology at Purdue University, where his research focuses on adaptive cybersecurity policy for AI-enabled systems. He is also the creator of the Adaptive Artificial Intelligence Risk and Assurance Framework, or AAIRAF. With more than 10,000 hours of public speaking, instruction, and panel moderation experience, Brian is known for making complex cybersecurity, technology, and risk topics practical and accessible.
Sessions
-
Panel: From Warning to Action - Defending Critical Infrastructure in Real TimeTuesday, October 6, 2026
1:30 PM - 2:15 PM
Carl Eshelman
Cyber Growth Leader, Americas - Honeywell
Carl Eshelman leads Honeywell’s Cyber Technical Solutions Consultant and Solution Architect team for the Americas. With more than 30 years of experience spanning IT infrastructure, networking, security, and industrial control systems, he is a recognized OT cybersecurity leader helping organizations across critical infrastructure and industrial sectors strengthen resilience in complex operational environments. Drawing on a broad, hands-on background across multiple technology domains, Carl brings a pragmatic perspective on how cyber risk impacts real-world operations and is known for cutting through industry buzzwords to deliver clear, experience-driven guidance on what actually works in OT cybersecurity.
Sessions
-
Beyond the Buzzwords: A Practical, Risk-Based Approach to What Actually Matters in OT CybersecurityMonday, October 5, 2026
12:35 PM - 1:10 PM
Carlos Sanchez
Fortinet, Director, OT Systems Engineering Specialist - Fortinet
Carlos-Raul Sanchez is a technologist with 32 years of experience in network, telecommunications, and critical infrastructure security. Carlos specializes in simplifying complex business problems with a pragmatic application of technology. With master’s degrees in computer science, business administration, and a wide range of experience ranging from US Air Force, DOD contractor, and O&G IT security, he is known for securing critical infrastructure worldwide. He spent 15 years leading teams securing oil fields in the United States and offshore assets in the Gulf of Mexico, Western Africa, Brazil, and South China Sea. He is the senior director of operational technology, providing solutions and education to companies seeking to improve their critical infrastructure security posture.
Sessions
-
Applying Network Detection and Response in OT without Breaking OperationsWednesday, October 7, 2026
1:30 PM - 2:00 PM
Christopher Goes
Researcher IV - Cybersecurity - National Laboratory of the Rockies
Chris Goes is an operational technology cybersecurity researcher focused on OT cyber ranges and the development of practical defensive capabilities for OT environments. He brings more than a decade of experience in OT cybersecurity, turning research into deployed solutions. Previously at Sandia National Laboratories, he is now with the National Lab of the Rockies in Golden, Colorado.
Sessions
-
Closing the Control-Layer Visibility GapWednesday, October 7, 2026
11:00 AM - 11:35 AM
CISA Speaker
CISA - U.S. Cybersecurity and Infrastructure Security Agency (CISA)
As the National Coordinator for Critical Infrastructure Security and Resilience, CISA works with partners at every level to identify and manage risk to the cyber and physical infrastructure that Americans rely on every hour of every day. CISA works with partners to defend against today’s threats and collaborate to build a more secure and resilient infrastructure for the future.
Sessions
-
CISA Threat Briefing: Lessons From Recent Critical Infrastructure IncidentsTuesday, October 6, 2026
11:00 AM - 11:35 AM -
Fortifying the Front Lines: Public-Private Readiness for an OT CrisisWednesday, October 7, 2026
3:50 PM - 4:20 PM
Clint Bodungen
Director, AI/ML Engineering - Arcova
Clint Bodungen is an OT cybersecurity pioneer and AI engineer with 30+ years of experience. Known for pioneering practical, innovative approaches to cybersecurity, he has spent the last two decade at the forefront of integrating gamification and AI into cybersecurity and training. He has published two books, Hacking Exposed: Industrial Control Systems and ChatGPT for Cybersecurity Cookbook, and created ThreatGEN® Red vs. Blue, an online cybersecurity simulation game, as well as AutoTableTop, an AI-driven incident response platform that uses AI to build and run IR tabletop exercises. Today, as Director of AI/ML Engineering at Arcova, his work centers on creating production-ready AI systems that help transform and modernize the cybersecurity industry.
Sessions
-
Building AI Agents for ICS/OT Security: From Zero to OrchestratorTuesday, October 6, 2026
10:10 AM - 5:10 PM
Cyrus Walker
Founder, CEO - https://www.Data-Defenders.com
Cyrus J. Walker III is Founder and CEO of Data Defenders, a cybersecurity firm serving municipalities, utilities, and public infrastructure operators, 501c3s, and SMBs. He brings thirty years of experience across cybersecurity operations, network architecture, digital forensics, and critical infrastructure protection. He serves on the DHS CISA Critical Infrastructure Partnership Advisory Council, Election Infrastructure Subsector, and holds an MIT Smart City Design certificate. He trained more than 5,000 law enforcement professionals under DHS funding, including NSA, FBI, and Secret Service personnel. Under his leadership, Data Defenders served as operational architect of Aurora, Illinois's cybersecurity operation from 2019 to 2025, water plant, traffic network, and CJIS systems.
Sessions
-
Dual-Scope Defense: A Six-Year Municipal IT + OT Engagement and What It BecameThursday, October 8, 2026
10:10 AM - 10:40 AM
Daniel Paillet
Senior Principle Cybersecurity Architect - Schneider Electric
Daniel Paillet is Senior Prinicple Cybersecurity Architect in Schneider Electric’s Energy Business Unit, focusing on secure‑by‑design solutions for energy and industrial systems. His experience spans U.S. Department of Defense programs and complex IT and OT environments across critical infrastructure, banking, retail, and point‑of‑sale systems. Daniel holds CISSP, CCSK, CEH, and ISA/IEC 62443 Cyber Security Expert certifications. He is a Senior Member of the International Society of Automation, an active contributor to ISA/IEC working groups, a member of the EC‑Council Global Advisory Board for Ethical Hacking, a published author, and has presented at industry security conferences on industrial cybersecurity and IEC 62443 adoption.
Sessions
-
The Cyber Resilience Act as a Catalyst for OT Cybersecurity ModernizationThursday, October 8, 2026
10:55 AM - 11:25 AM
Daniel Paré
Principal Product Manager, Industrial OT Security - Palo Alto Networks
Daniel Paré is a Principal Product Manager, Industrial OT Security at Palo Alto Networks where he focuses on building tools to help industrial organizations maintain operational uptime by securing their mission critical systems. Prior to joining Palo Alto Networks Daniel spent time at GE and Siemens building Industrial IoT systems and software. Daniel completed his graduate engineering work at Stanford University and undergraduate work at the University of California, Davis.
Sessions
-
AI-Accelerated Exploits and the Case for Pre-Disclosure Virtual Patching in OTWednesday, October 7, 2026
1:30 PM - 2:00 PM
David Formby
CEO/CTO - Fortiphyd Logic Inc
David Formby is CEO/CTO and co-founder of Fortiphyd Logic. He received his Ph.D. from the Georgia Institute of Technology where he focused on developing novel attacks and defenses for industrial control system networks and PLCs. Formby now leads Fortiphyd Logic in developing innovative solutions for industrial cybersecurity training and PLC endpoint detection. He is a member of the ISA and the Top 20 Secure PLC Coding Practices community.
Sessions
-
Testing Your DERs Before an Attacker Does: Fuzzing DNP3, SunSpec, and IEEE 2030.5Wednesday, October 7, 2026
9:40 AM - 10:10 AM
Domenic Busa
Senior Manager, Solutions Engineering - Johnson Controls
Domenic Busa is a Senior Manager at Johnson Controls, where he leads pre-sales and solution architecture for the OpenBlue Airwall zero trust OT cybersecurity platform. His path runs from manufacturing and controls engineering through industrial edge AI to operational technology security. He works regularly with controls engineers, facilities directors, and security leaders, is a named inventor on multiple US patents, and holds a B.S. in Mechanical Engineering from Marquette University.
Sessions
-
Reconnaissance Denial in OT: Using the Host Identity Protocol to Deny Asset DiscoveryWednesday, October 7, 2026
3:15 PM - 3:45 PM
Donovan Tindill
Sr Dir, OT Cybersecurity - DeNexus
Donovan is Sr Director and Subject Matter Expert (SME) at DeNexus. He spent over 17 years as a customer-facing ICS/OT cybersecurity consultant, and another 5 years in Product Management with direct leadership over Honeywell's ICS/OT cybersecurity products, consulting and managed security services. Donovan now provides industry expertise for DeNexus’ DeRISK platform. From startups to large public companies, he has been a major contributor to the OT cybersecurity community since 2000 including ISA-99/62443 author/contributor/trainer, Vice-Chair for DHS Industrial Control Systems Joint Working Group (ICSJWG) Steering Team (IST); Public Safety Canada ICS Security Symposium Advisory Committee member and advisor to universities building ICS/OT cybersecurity curriculums.
Sessions
-
The Cyber-Physical Balance Sheet: Managing OT Cyber Risk, Insurance, and ResilienceTuesday, October 6, 2026
2:20 PM - 2:50 PM -
From Dwell Time to Dollars: Quantifying the Financial Value of Faster OT Incident RecoveryThursday, October 8, 2026
12:00 PM - 12:30 PM
Douglas Woolf
Principal - Dark Wolf
CISSP and CISM-certified cybersecurity architect, analyst, and researcher with 10+ years of experience delivering mission-grade security across defense, enterprise, and R&D environments. I specialize in modern, RMF-driven assessment and authorization for innovative organizations and their advanced technologies. From architecting post-quantum cryptography solutions to securing emerging photonic compute fabrics, I translate complex technical risk into clear, actionable decisions for authorizing officials and stakeholders.
Sessions
-
Photonics for Resilient OT SecurityWednesday, October 7, 2026
2:40 PM - 3:10 PM
Dr. Ken Reaves
Managing Director - Relate Central
Dr. Kenneth Reaves is a cybersecurity executive and researcher with 25+ years of experience leading technology, security, and digital transformation initiatives. He is the Founder of Relate Central, delivering cybersecurity, risk management, and AI-driven solutions. Dr. Reaves earned his DBA from Georgia State University – J. Mack Robinson College of Business, where his research examines why cybersecurity investments fail. His work bridges executive decision-making and operational security, with a focus on critical infrastructure resilience. He is a frequent speaker at academic and industry conferences, known for delivering practical, real-world insights.
Sessions
-
Why ICS Cybersecurity Investments Fail in Critical InfrastructureMonday, October 5, 2026
2:35 PM - 3:10 PM
Dylan Hinz
Associate Principal Cyber Analyst, Darktrace - Darktrace
Dylan Hinz is an Associate Principal Cyber Analyst at Darktrace with more than five years of experience in threat detection, cloud security, and adversary behavior analysis. Dylan contributed to Darktrace’s energy‑sector research, including the 2024–2025 State of Cyber Security in Energy reports, focusing on emerging attack vectors targeting U.S. critical infrastructure. Holding the SANS GRID certification, Dylan specializes in industrial control system defense and the IT/OT intersection. Dylan’s work spans hands‑on investigations, hypotheses‑driven threat hunts, and detection strategy development for complex cloud and hybrid environments. Drawing on real‑world energy‑sector incidents, Dylan advises organizations on threat evolution and how AI‑assisted defense can reduce operational risk.
Sessions
-
How Cloud Expansion and AI‑Driven Threats Are Reshaping Cyber Risk in the U.S. Energy SectorThursday, October 8, 2026
2:55 PM - 3:25 PM
George Urling
Intelligence Analyst - West Virginia Department of Homeland Security - West Virginia Fusion Center
George Urling is an Intelligence Analyst for the West Virginia Department of Homeland Security’s West Virginia Fusion Center (WVFC). He serves as a Deputy Coordinator for the National Fusion Center Association Cyber Intelligence Network and oversees the Southeast Region of the US. George holds a master's degree in Cybersecurity and a bachelor’s degree in Cyber Forensics and Security from Marshall University. In his current role, he serves on the Threat Intelligence Unit at the WVFC and constantly researches emerging threats, cyber and physical, facing West Virginia and the US.
Sessions
-
The Need for OSINT in OT SecurityTuesday, October 6, 2026
2:20 PM - 2:50 PM

Glen Combe
Fortinet, OT Specialist Systems Engineer - Foritnet
Glen Combe has 26 years of experience in IT and OT operations and has dedicated his career to architecting and implementing secure cybersecurity solutions for operational technology environments. His passion lies in building and optimizing cybersecurity frameworks that align with business objectives while protecting critical infrastructure. Glen specializes in evaluating IT/OT systems, identifying vulnerabilities, and applying tailored security controls to mitigate risks. At Fortinet, he brings deep expertise in industrial cybersecurity, IT/OT convergence, and risk management to drive resilient and future-proofed security solutions.
Sessions
-
Solutions Theater (Demo): Secure Remote Access for Operational TechnologyTuesday, October 6, 2026
11:40 AM - 12:10 PM -
Solutions Theater(Demo): Seeing Clearly Through Segmentation: Strengthening Industrial CybersecurityWednesday, October 7, 2026
10:15 AM - 10:45 AM -
Solutions Theater (Demo): Using the Right Signals to Protect and Manage OT Network TrafficThursday, October 8, 2026
9:35 AM - 10:05 AM
Glenda Snodgrass
President - TNE
Glenda R. Snodgrass has been President, lead consultant and project manager at The Net Effect since the company's inception in 1996. She is a Certified Information Security Manager (CISM), CMMC Certified Professional (CCP), CMMC Certified Assessor (CCA), Lead CCA, and ITAR Export Control Professional (ECoP®) specializing in helping organizations meet their security and compliance requirements. She has conducted numerous workshops covering GLBA, PCI DSS, HIPAA, FAR 52.204-21, DFARS , NIST 800-171, NIST CSF and CMMC. Her dynamic personality and effective teaching style have made her a sought-after public speaker and corporate trainer for more than twenty years.
Sessions
-
OT/IOT in CMMCWednesday, October 7, 2026
10:15 AM - 10:45 AM
Hazel Cerra
Director of Digital Security Convergence - BlackCloak
Hazel Cerra’s mission is to connect people, ideas, and strategies that protect and empower organizations in an increasingly complex digital world. After more than 25 years as a Special Agent with the U.S. Secret Service, protecting high-risk individuals and investigating cyber-enabled financial crimes, Hazel saw firsthand that threats don’t just target systems, they target people. Today, as Director of Digital Security Convergence at BlackCloak, she helps executives, boards, and high-net-worth individuals protect their personal digital lives, from devices and home networks to family security. Her work sits at the intersection of cybersecurity, executive protection, and threat intelligence, helping organizations close the gap between corporate security and personal risk.
Sessions
-
From Presidential Protection to Digital Executive Protection: Convergence of Physical and DigitalThursday, October 8, 2026
9:35 AM - 10:05 AM
Hector Perez
Head of Strategy, Global Industrial Cybersecurity - Black & Veatch
Hector is the Head of Strategy for Black & Veatch’s Industrial Cybersecurity practice. With more than 20 years of experience at the intersection of operational technology (OT) cybersecurity, engineering and digital transformation, he drives strategic innovation to enhance cyber resilience across complex industrial environments. Hector specializes in secure-by-design methodologies that align operational goals with evolving threat landscapes. Throughout his career, he has earned multiple industry awards and patents, and his contributions to high-performance system design and cybersecurity integration have helped shape best practices across critical infrastructure organizations. Hector holds a degree in Chemical Engineering and an MBA from Rice University.
Sessions
-
Cyber Risk Quantification for Critical Infrastructure: Moving Beyond ROI to Risk-Informed DecisionsTuesday, October 6, 2026
2:55 PM - 3:25 PM
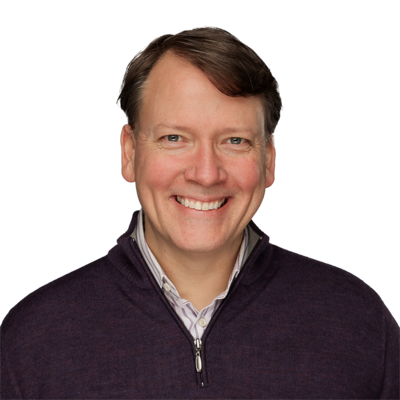
Ian Bramson
Vice President, Global Industrial Cybersecurity - Black & Veatch
Ian Bramson is vice president of Black & Veatch’s Global Industrial Cybersecurity Practice, responsible for the strategy, commercialization and business growth of all the company’s integrated cybersecurity solutions and capabilities. He’s a highly experienced leader in the fields of cybersecurity, risk management, and digital transformation with a career spanning over 25 years. Ian works closely with top-level executives in critical infrastructure industries to provide innovative solutions that minimize cybersecurity risks. He has successfully built two cybersecurity consulting services over the past decade, both of which were supported by global sales organizations and implemented in multiple industries.
Sessions
-
Agentic AI in Critical Infrastructure: Redefining OT Cybersecurity in ICS EnvironmentsThursday, October 8, 2026
9:00 AM - 9:30 AM
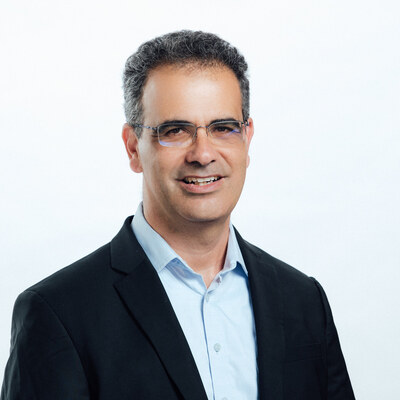
Ilan Barda
CEO - Radiflow
Ilan is a seasoned ICT & Cyber executive. Ilan is the founder and CEO of Radiflow, a leading vendor of OT Security solutions. Before starting Radiflow, Ilan served as the CEO of Seabridge, a Nokia-Siemens Networks subsidiary.
Sessions
-
Using AI to Automate Exposure Assessment in OT sitesThursday, October 8, 2026
10:55 AM - 11:25 AM
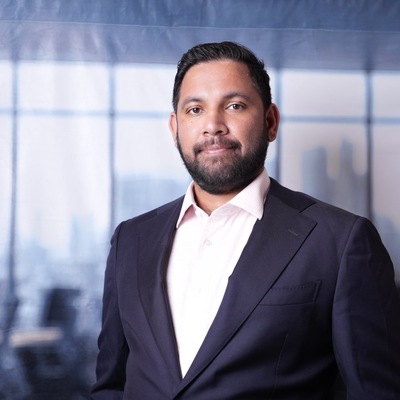
Jagannathan Raghunathan
Director Cyber Physical Security - Bureau Veritas
Jagan is a cyber physical security leader with over 15 years of experience across operational technology (OT), industrial control systems (ICS), engineering, and cybersecurity consulting. His background spans manufacturing, renewable energy, critical infrastructure, and transformation programs, with experience supporting both asset owners and global consulting organizations. He currently leads Cyber Physical Security Services for North America at Bureau Veritas Cybersecurity, focusing on strategy, cyber-informed engineering, operational resilience, and at scale assurance programs. Jagan has held leadership and roles across OT security engineering, operations, in consulting, and industrial environments, bringing a practical perspective that bridges strategy with operational realities
Sessions
-
Cybersecurity Commissioning: The OT Discipline Nobody OwnsMonday, October 5, 2026
2:00 PM - 2:35 PM
Jon "McFly" McEllroy
Offensive/Defensive Cyber Engineering Team Lead - Modern Technology Solutions, Inc. (MTSI)
Jon "McFly" McEllroy is a retired US Naval Officer of 22 years serving as a carrier jet pilot, test pilot, acquisition professional, and hands-on Cyber SME for aircraft, ships, and weapons. He has extensive experience in as well as teaching software reverse engineering, vulnerability research, exploit development, and software defined radio. Currently he leads the Offensive/Defensive team in MTSI's Cyber Physical Systems (CPS) group as well as being the Adversarial Cyber Test Tech Fellow for MTSI. His hobbies include smoking meats, amateur cocktail mixing, and writing ROP chains in assembly.
Sessions
-
Cyber Attack Methods for Cyber-Physical Systems (3-Day Course)Tuesday, October 6, 2026
10:10 AM - 5:10 PM
Josh Ross
Co-Founder & CEO - Ironloop
Josh Ross is the Co-Founder & CEO of Ironloop, a cybersecurity startup helping manufacturing, energy, and defense keep operations secure and audit-ready. Ironloop turns industrial machine and network configurations into a continuously updated inventory, change alerts, and compliance-ready documentation, so teams can reduce risk without disrupting production. Before Ironloop, Josh led cloud infrastructure at Applied Intuition, where he built deployment automation, monitoring, and observability systems across cloud and on-prem environments, including government and defense networks. He holds a degree in computer science and economics from the University of Pennsylvania and is based in New York City.
Sessions
-
Target Rich, Cyber Poor: Raising the OT Security Baseline As Attacks Get CheaperMonday, October 5, 2026
12:00 PM - 12:35 PM
Juan Lopez JR
Lead Technical SME, Critical Infrastructure Security & Resilience Research - Oak Ridge National Laboratory
Dr. Juan Lopez Jr. is a cybersecurity leader serving as the Lead Technical SME for the DHS Science & Technology Directorate’s Critical Infrastructure Security & Resilience Research (CISSR) program, where he focuses on industrial control systems and open‑source software security. He previously led ORNL’s Energy and Control Systems Security group and managed its Cyber‑Physical R&D portfolio, advancing national‑level research in critical infrastructure protection, nuclear cybersecurity, and RF‑DNA fingerprinting. Dr. Lopez holds a Ph.D. in Computer Science from the Air Force Institute of Technology along with multiple professional certifications including CISSP, CSSA, and Scrum Master, and is a retired U.S. Marine Corps veteran with 27 years of service.
Sessions
-
AI-Powered Attacks on ICS SBOMsThursday, October 8, 2026
11:30 AM - 12:00 PM
Karthik Thumula
Director of Technical Marketing Engineering - Palo Alto Networks
Karthik Thumula is a Director of Technical Marketing Engineering from Palo Alto Networks focusing on IoT Security. In his current role as a PTME, Karthik drives all the sales and partner enablement. He helps customers with High-Level Designs, PoCs and deployments. Prior to joining Palo Alto Networks, Karthik worked as a Technical Marketing Leader in NAC, switching, fabric and SDN products. He holds a Masters degree in Computer Science and is a double CCIE.
Sessions
-
AI Found It & We Stopped It: Live OT Virtual Patching DemoTuesday, October 6, 2026
11:00 AM - 11:35 AM
Keon McEwen
Head of Solutions Development, Global Industrial Cybersecurity - Black & Veatch
Keon is the Head of Solutions Development at Black & Veatch’s Industrial Cybersecurity practice. His expertise includes cybersecurity, control systems, automation and data. He brings a unique combination of technical expertise and market development acumen to help companies achieve success during pivotal moments of change. At ABS Group, he designed, built and managed their Industrial Security Operations Center (ISOC) and under his leadership, the ISOC expanded globally to 20+ countries and grew the customer base across critical infrastructure industries such as Power, Oil & Gas, Transportation and Manufacturing. Keon has a strong knowledge in OT/ICS systems, related compliance requirements and guidelines (NERC CIP, IMO) and cybersecurity frameworks (NIST, ISA/IEC 62443, ISO).
Sessions
-
Operational Data Meshing for Critical Infrastructure: Advancing OT Detection and Response in ICS EnvThursday, October 8, 2026
2:20 PM - 2:50 PM
Kevin Kumpf
Chief OT Strategist / Consultant - Kasm Technology
I am currently an industry consultant and the Chief OT Strategist, for Kasm Technology. With more than 20 years of IT / OT experience I have worked as a true problem solver at some of the top vendors in the OT realm helping define product strategy, addressed challenging customer safety and security issues and building programs to meet regulatory and compliance challenges. Past roles have also included Director of OT Security at Iberdrola N.A., and as the lead strategist and consultant for manufacturing, energy and cloud service providers, where I built their threat and vulnerability programs as well as built incident response teams.
Sessions
-
Why the “C” of AIC for OT/ICS is becoming more critical in the age of industrial modernizationWednesday, October 7, 2026
11:40 AM - 12:15 PM
Lasse Lundstad
Senior OT Cybersecurity Consultant - DNV
Lasse Lundstad is a Senior Cybersecurity Consultant at DNV, specialising in governance, risk, and compliance across industrial environments. He began his career in sales, marketing, and public procurement, where his interest in security developed into a focus on cybersecurity. At DNV, he has worked across IT and operational technology (OT), supporting clients in oil and gas, aquaculture, and offshore wind, with experience in ISO 27001, NIST, NIS2, and IEC 62443. He is currently contributing to initiatives focused on strengthening cybersecurity in critical infrastructure, including a Joint Industry Project on implementing IEC 62443 in offshore wind.
Sessions
-
Joint Industry Project - OT Cybersecurity for Offshore WindThursday, October 8, 2026
1:45 PM - 2:15 PM
Leonard Kershteyn
Director of Product Management Cybersecurity - Honeywell International Inc
Leo Kershteyn, CISSP, GICSP is Director of Product Management with over a decade of experience in the industrial cybersecurity sector. He has been closely involved in Honeywell’s strategic cybersecurity portfolio realignment and M&A of an OT intrusion detection platform that has since evolved into Honeywell’s flagship industrial cybersecurity offering. Leo began his career as an Electrical Engineer and brings deep technical expertise across cybersecurity, OT threat detection, and critical infrastructure protection. He currently resides in the Atlanta, Georgia metropolitan area.
Sessions
-
Actioning Threat Intelligence: Tuning Intrusion Detection Systems for Nation State AttacksThursday, October 8, 2026
9:00 AM - 9:30 AM
Mackenize Morris
Principal Industrial Consultant - Dragos
Mackenize Morris is a Principal Industrial Consultant at the industrial cybersecurity company Dragos, Inc. where he assists the professional services teams in conducting network and vulnerability assessments. Previously, Mackenize worked as a chemical engineer and system architect and administrator for a DOE contractor for a DCS system until fully switching over to an ICS cybersecurity position within the DOE complex. Mackenize received his B.S. in Chemical Engineering and MBA from the University of South Carolina as well as a Masters in Information Security Engineering from the SANS Technology Institute. He currently holds a dozen GIAC Certifications. Mackenize’s name is pronounced like Mackenzie; the IZE spelling was a result of a spelling error on his birth certificate.
Sessions
-
AI-Augmented Attacks on Industrial Control Systems and the Road AheadWednesday, October 7, 2026
2:40 PM - 3:10 PM
Mary Gannon
Director of OT Resilience - Copia Automation
Mary Gannon is a global OT/ICS cybersecurity leader, specializing in industrial incident response, critical infrastructure protection, and cyber risk management. She started her career 13 years ago in Emergency Management and Community Risk Reduction, concentrating on physical and cyber-physical threats. She has worked in a variety of roles including the Global OT Security Leader for two critical manufacturers, as well as consulting roles focusing on OT security, incident response, and incident management. Since its formation, Mary has served as the Incident Commander, Facilitator, and Subject Matter Expert of ICS4ICS. Mary is a CompTIA CSTAC leader and exam development SME for the upcoming SecOT+ exam. She holds her GRID, GICSP, + GPEN certifications.
Sessions
-
Breakfast Panel Session: Evolutionary ResilienceWednesday, October 7, 2026
8:10 AM - 8:55 AM
Matt Davis
Control Systems Section Manager - HDR
Matt Davis is a Section Manager and Control Systems Engineer with HDR, where he leads a team of automation engineers and specializes in the planning, design, and implementation of industrial control systems for water and wastewater facilities. His experience spans PLC, SCADA, industrial networking, and control system modernization for utilities across the United States. Matt is passionate about developing practical, reliable automation solutions and helping clients navigate the technical and operational challenges of modernizing critical infrastructure.
Sessions
-
ICS / OT Stands the Cybersecurity CIA Triad on Its HeadMonday, October 5, 2026
4:30 PM - 5:05 PM
Matt Lucas
CEO - RedEye Security
Matt Lucas is the founder of RedEye Security, a Nashville-based firm focused on detection engineering and exposure reduction for operational technology and critical-infrastructure environments. He runs an ongoing ICS exposure research effort that maps internet-facing industrial devices across U.S. sectors, publishes daily OT and ICS threat intelligence, and has brought hands-on "here is your exposure" demonstrations directly to regional operators and county-level events. His work focuses on the unglamorous, high-impact basics: finding what is exposed before an adversary does, and the low-cost fixes that close most of the gap.
Sessions
-
Your Control Network Is Already Exposed, and Attackers Are Just WaitingWednesday, October 7, 2026
10:15 AM - 10:45 AM
Matt Malone
ICS Cybersecurity Consultant - Yokogawa
After graduating from Texas A&M, Matt embarked on his eight-year career in the U.S. Navy as a salvage diver and bomb disposal technician. He completed three overseas deployments, two of which were combat deployments. He returned home to Texas to begin a career in sales before transitioning to project management. During his time as a project manager, he caught the cybersecurity bug and changed his master’s thesis to address the current state of industrial cybersecurity in North America. He has since devoted his career to learning everything possible about how to secure industrial control systems against cyberattacks. Matt joined Yokogawa in April of 2020, earned his GICSP certification soon after, and is passionate about securing ICS networks.
Sessions
-
Cyber Attack and Process SafetyWednesday, October 7, 2026
3:15 PM - 3:45 PM
Pavlo Chernikov
Critical-Infrastructure Cybersecurity Researcher & Practitioner (former Director, SME "Kyivteleservis") - Independent Researcher
Pavlo Chernikov directed the Kyiv municipal enterprise responsible for the city government's critical-infrastructure networks, operational telemetry, command-and-control, and digital-service continuity (2021-2024) - including utility/municipal IoT (LoRaWAN) and city-scale public-safety systems - sustained through active wartime cyber and kinetic attack across more than 1,800 institutions. He is a peer-reviewed researcher in critical-infrastructure resilience, with published work on operational resilience of municipal infrastructure under hostilities and on LoRaWAN resilience under electronic-warfare interference. ORCID: 0009-0006-7390-9698.
Sessions
-
OT Resilience Under Cyber-Kinetic Attack: Lessons from a Wartime CapitalTuesday, October 6, 2026
11:35 AM - 12:15 PM
Qiang Huang
VP, Product Management - Palo Alto Networks
Qiang Huang is the VP of Palo Alto Networks's IoT and OT security products and solutions. He has over 30 years of deep experience in a wide range of technologies including network security, enterprise networking, and IoT and OT. In recent years, Qiang incubated several industry-first IoT and OT products and solutions, and developed partnerships across industries such as manufacturing, energy, transportation, and smart cities.
Sessions
-
OT in the Crosshairs: Protecting Critical Infrastructure in the Age of Frontier AI-Powered AttacksTuesday, October 6, 2026
9:35 AM - 10:10 AM
Rafael Narezzi
CEO & Co-Founder - Centrii
Rafael Narezzi is the Founder of Centrii and an OT cybersecurity expert with over 20 years of experience leading technology, cybersecurity and digital transformation for global enterprises. He has played a key role in growing Centrii into a trusted managed security services provider, supporting global clients including FTSE 100 companies and major private equity firms. Previously, as Group CTO at CFP Energy and CIO at NextEnergy Capital / Wise Energy, Rafael led technology innovation, applying AI, machine learning and data analytics to improve operational performance and create new commercial opportunities. He also founded the South America Cyber Security Summit and is a regular international speaker and guest lecturer.
Sessions
-
Quantifying OT Cyber Risk in Financial Terms: Executive Action in Critical Energy InfrastructureWednesday, October 7, 2026
2:05 PM - 2:35 PM
Ram Rajagopalan
Founder CEO - neuralcy
Ram Rajagopalan is the Founder and CEO of Neuralcy, an AI security company focused on detecting and neutralizing threats to AI agents operating in critical infrastructure, OT/IoT, and physical AI environments. He leads original research into steganographic attack channels against Vision Language Models and multi-agent systems, with provisional patent applications covering multimodal hidden-prompt detection and runtime AI agent defense mechanisms. Prior to Neuralcy, he held senior technology leadership roles across enterprise software and infrastructure at Amazon, Qualcomm, ResMed, Jina AI, Appen AI and Hughes
Sessions
-
Ghost in the Grid: Hijacking AI Agents Through Hidden Channels in OT/ICS NetworksWednesday, October 7, 2026
3:50 PM - 4:20 PM
Rupesh Shirke
Associate Principal - LTIMindtree
Rupesh Shirke is a distinguished Operational Technology (OT) and Industrial Control Systems (ICS) cybersecurity leader with over 17 years of experience safeguarding critical infrastructure. A PhD Candidate specializing in the integration of Artificial Intelligence with OT security, Rupesh bridges the gap between scholarly research and industrial reality. As a Principal Architect and CISSP, he designs enterprise-scale defense architectures aligned with ISA/IEC 62443. Driven by a deep passion for cyber-physical safety and mitigating kinetic risks, Rupesh is dedicated to protecting the vital global energy, water, and manufacturing systems that power our communities.
Sessions
-
Designing Zero-Trust Cross-Domain Identity Architectures for Converged IT/OT Active DirectoryThursday, October 8, 2026
11:30 AM - 12:00 PM

Sai Molige
Forescout Technologies Inc
Sai Molige, also known as Cyb3rhawk, is Senior Manager of Threat Hunting at Forescout Technologies, where he leads threat hunting research, incident response, and adversary infrastructure operations. His work focuses on understanding attacker behavior and translating threat intelligence into practical, repeatable approaches for threat hunting and detection engineering. Sai has held cybersecurity roles at Comcast and Snap Inc. and has extensive experience investigating ransomware, advanced threat activity, exploitation campaigns, and threats spanning IT, IoT, and operational technology environments. He is an active security researcher and community contributor who regularly publishes technical research and shares practical methodologies for threat hunting, detection engineering, DFIR, and cyber threat intelligence.
Sessions
-
From Crash to Code Execution: Inside an AI-Assisted PLC Exploit PortTuesday, October 6, 2026
3:30 PM - 4:00 PM
Shwetha GC
OT Cybersecurity Lead - Siemens Energy
Shwetha Gowdanakatte is an OT cybersecurity professional specializing in securing cyber-physical systems and critical infrastructure. She has hands-on experience implementing IEC 62443 controls in digital substations, focusing on access control, PKI, network segmentation, and remote access security, threat modeling, risk assessment including red and blue team activities . She has led lab cybersecurity certification efforts and develops audit-ready security solutions in operational environments. She is currently a Ph.D. candidate researching AI-driven threat modeling and access control in cyber-physical systems, with publications at ACSAC, IEEE and CIGRE. Her work bridges theory and practice, enabling organizations to operationalize cybersecurity standards effectively.
Sessions
-
Practical Implementation of IEC 62443 in Cyber-Physical Systems: Bridging Compliance and Real-WorldWednesday, October 7, 2026
2:05 PM - 2:35 PM
Stephen Mozia
Sr.Manager - PwC
Stephen Mozia, CISSP is an experienced professional who has helped guide companies through their cybersecurity, asset reliability, and digital transformation journeys across most critical infrastructure industries. Mozia is currently a Sr. Manager within PwC where he helps clients secure their OT infrastructure. Mozia previously spent his career working in consulting, engineering, and business development capacities with the cybersecurity company, Optiv, and automation vendors, Rockwell Automation and Emerson. Mozia’s focus has always surrounded securing and digitally transforming organizations through supporting innovative technologies around asset management, cyber risk management, network architecture/design, data management, analytics, augmented/virtual reality, and automation.
Sessions
-
From Pumps to PLCs: A Reliability-Centered Approach to Cyber Risk ManagementMonday, October 5, 2026
1:10 PM - 1:45 PM
Steve Johnson
Sr. Control Systems Cybersecurity Specialist - HDR
Steve Johnson, MSc, CISSP, C|CISO Steve earned his MSc in Cybersecurity from Essex University in Colchester, England, following a career in the U.S. Army as a Communications Security Specialist. He has over 20 years of experience in the design of large-scale intelligent transportation systems, including 7 years as the program manager and principal investigator for a USDOT research project on Connected Vehicle technology. Steve currently leads cybersecurity design and consulting services for several state DoTs, transit rail operators, and aviation facilities. He also leads cybersecurity design projects for the Department of War pertaining to building management systems. He is a Professional Associate at HDR, a large A&E firm.
Sessions
-
ICS / OT Stands the Cybersecurity CIA Triad on Its HeadMonday, October 5, 2026
4:30 PM - 5:05 PM
Terry McCorkle
CEO & Founder - PhishCloud, Inc
Terry is the Founder and CEO of PhishCloud Inc, a proactive intelligence delivery company. He is a certified hacker with over twenty-one years of experience in the cybersecurity industry and has served in a broad range of technical, analytical, and leadership roles. He is passionate about his family, employees, and helping people in cybersecurity. Terry loves entrepreneurship and, as CTO and Co-Founder of Spearpoint Security, helped lead through an acquisition by Cylance in 2013. He holds a BS in Information Technology from Capella University and several cybersecurity certifications.
Sessions
-
East - West Detection Engineering in OT EnvironmentsTuesday, October 6, 2026
3:30 PM - 4:00 PM
Tom Sego
CEO - BlastWave
Tom Sego is the CEO of BlastWave, an OT cybersecurity company focused on Zero Trust protection for industrial control systems and critical infrastructure. He has spent his career at the intersection of operational technology and cybersecurity, working with energy, manufacturing, water, government, and transportation organizations across 21 countries. BlastWave has analyzed 23 of the most significant OT cyberattacks in recorded history (the BlastWave Hackopedia), and Tom draws on that dataset regularly in industry discussions, webinars, and public commentary. Tom speaks frequently on the intersection of AI and OT security: both the threat dimension (how AI is changing the attacker toolkit) and the defense dimension (why AI-powered defensive automation requires a different risk model in OT).
Sessions
-
23 Attacks. 3 Controls. A Decade of OT Breaches and the Pattern Nobody Talks AboutThursday, October 8, 2026
10:10 AM - 10:40 AM
Tyler Berube
Senior OT Platform and Security Engineer - Microsoft
Tyler Berube is a Senior OT Security Engineer at Microsoft, where he focuses on industrial control system and operational technology security for cloud and datacenter operations. He came into the discipline from the floor, moving through critical facilities technician, critical environment instrumentation, and critical infrastructure platform engineering roles before specializing in OT security. His current work covers consequence-driven engineering, OT and ICS architecture review, identity and access management for control system environments, and the secure integration of new mechanical, electrical, and automation technologies into operating fleets. He partners with mechanical, controls, and platform engineering teams to make consequence analysis a routine part of design and operations.
Sessions
-
Engineering Out the Adversary: Applying Consequence-Driven Cyber-Informed Engineering (CCE)Wednesday, October 7, 2026
11:00 AM - 11:35 AM
Umang Barman
OT specialist - Zscaler
Umang Barman focuses on OT and industrial cybersecurity, working closely with manufacturing and critical infrastructure organizations. His work centers on reducing operational risk in complex factory and plant environments. With experience across network, identity, data, and SecOps, he brings a unique perspective that helps align network, security, and OT teams.
Sessions
-
Faster Than You Can Watch: Why Agentic AI Breaks the OT Visibility ModelWednesday, October 7, 2026
11:40 AM - 12:15 PM
Vivek Ponnada
SVP Growth & Strategy - Frenos
Vivek Ponnada is an Operational Technology (OT) Security practitioner with global experience and serves as SVP of Growth & Strategy at Frenos. Having started his career in Industrial Control Systems (ICS) as a Technician, Vivek became a Controls Engineer and commissioned Gas Turbines in Europe, Middle-East, Africa and South-East Asia. Post MBA, Vivek held multiple roles including Sales, Marketing & Business Development and Services covering OT Security solutions for Critical Infrastructure industries at GE, XenonCyber Dynamics and Nozomi Networks. Vivek has a C.Eng from I.E. India, MBA from UT-Austin and hold the ISA/IEC 62443 Cybersecurity Expert & GICSP certifications. He is a member of the ISA, ISACA, Public Safety Canada ICS Security Symposium Advisory Committee and is a CS2AI Fellow.
Sessions
-
Frontier vs. Local LLMs for OT Security - Considerations & Use CasesWednesday, October 7, 2026
2:05 PM - 2:35 PM