



When Vulnerability Discovery Outpaces Patching: AI-Assisted Research in ICS Protocol Libraries
About This Session
The timeline for finding vulnerabilities in C/C++ protocol software is compressing. The timeline for safely remediating them in industrial environments is not.
This session examines that discovery–remediation gap through human-led, AI-assisted vulnerability research in open-source ICS and critical-infrastructure libraries. It draws on 2026 CERT/CC-coordinated disclosures covering 18 CVEs across o6 Automation open62541, MZ Automation libIEC61850, OFFIS DCMTK, and GDCM. The core ICS case studies focus on OPC UA and IEC 61850/MMS software; the DICOM cases are used as adjacent examples of the same supply-chain pattern in safety- and availability-sensitive environments.
The practical issue for asset owners is not that “AI can hack ICS.” It is that AI can accelerate the front end of vulnerability research while the back end remains constrained by vendor triage, safety validation, maintenance windows, incomplete asset inventories, and hidden third-party dependencies inside commercial products, gateways, engineering tools, and test systems.
I will explain the human-led review process behind the findings, including Refute-or-Promote — an adversarial validation workflow that filters candidate findings before disclosure. The methodology is documented in arXiv:2604.19049 and is designed to separate plausible-looking defects from reproducible, operator-relevant vulnerabilities before reports reach vendors, maintainers, or CERTs. That distinction matters in OT: the cost of being wrong is wasted triage, but the cost of being slow is prolonged exposure in environments where patching may depend on safety validation and outage windows.
Attendees will leave with a practical framework for reducing time to understand exposure when patching cannot happen in time: demanding protocol-library coverage in vendor SBOMs, prioritizing compensating controls for protocol-facing attack surfaces, and building faster coordination among researchers, CERTs, vendors, and asset owners.
The session closes with a structured approach for acting on disclosed vulnerabilities when industrial remediation timelines are measured in quarters, not weeks.
This session examines that discovery–remediation gap through human-led, AI-assisted vulnerability research in open-source ICS and critical-infrastructure libraries. It draws on 2026 CERT/CC-coordinated disclosures covering 18 CVEs across o6 Automation open62541, MZ Automation libIEC61850, OFFIS DCMTK, and GDCM. The core ICS case studies focus on OPC UA and IEC 61850/MMS software; the DICOM cases are used as adjacent examples of the same supply-chain pattern in safety- and availability-sensitive environments.
The practical issue for asset owners is not that “AI can hack ICS.” It is that AI can accelerate the front end of vulnerability research while the back end remains constrained by vendor triage, safety validation, maintenance windows, incomplete asset inventories, and hidden third-party dependencies inside commercial products, gateways, engineering tools, and test systems.
I will explain the human-led review process behind the findings, including Refute-or-Promote — an adversarial validation workflow that filters candidate findings before disclosure. The methodology is documented in arXiv:2604.19049 and is designed to separate plausible-looking defects from reproducible, operator-relevant vulnerabilities before reports reach vendors, maintainers, or CERTs. That distinction matters in OT: the cost of being wrong is wasted triage, but the cost of being slow is prolonged exposure in environments where patching may depend on safety validation and outage windows.
Attendees will leave with a practical framework for reducing time to understand exposure when patching cannot happen in time: demanding protocol-library coverage in vendor SBOMs, prioritizing compensating controls for protocol-facing attack surfaces, and building faster coordination among researchers, CERTs, vendors, and asset owners.
The session closes with a structured approach for acting on disclosed vulnerabilities when industrial remediation timelines are measured in quarters, not weeks.
Speakers
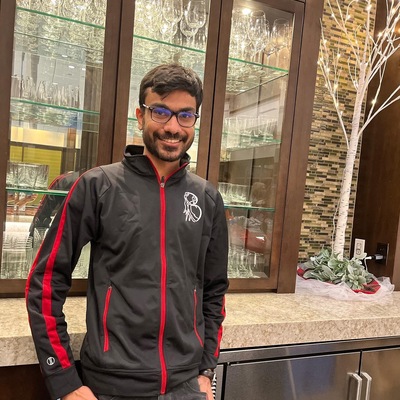
Abhinav Agarwal
Sr Software Engineer - Rubrik
Abhinav Agarwal is an independent security researcher, software engineer at Rubrik, and open-source maintainer. His work focuses on vulnerability discovery, secure-by-default engineering, and the security maturity of widely deployed software. He has reported vulnerabilities across AI infrastructure, cloud platforms, cryptography, Linux/open-source components, and ICS/OT software, including issues coordinated through CISA and major vendors. He is a maintainer of sshfs and a collaborator in the libfuse ecosystem.
His past talks include "Highly Scalable, Masterless, Distributed File System at Rubrik" at SDC 2025 and "SymEngine A Fast Symbolic Manipulation Library" at Scipy 2016
His past talks include "Highly Scalable, Masterless, Distributed File System at Rubrik" at SDC 2025 and "SymEngine A Fast Symbolic Manipulation Library" at Scipy 2016
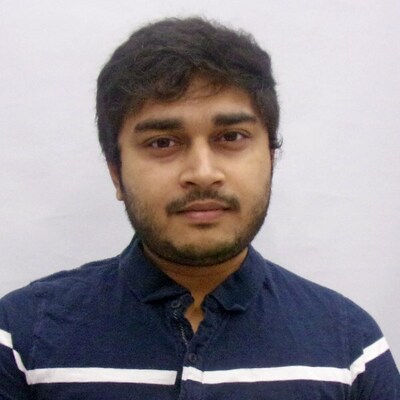
Akshat Sinha
Site Reliability Engineer - Rubrik
A site-reliability engineer and security researcher focused on the infrastructure layer of AI and cloud-native systems. Akshat's work pairs hands-on vulnerability research with measurement — how engineering-maturity gaps in fast-adopted software become exploitable attack surface — with responsible disclosure across open-source AI platforms, language sandboxes, and infrastructure tooling.